Six principles before installation
Judge by purpose and operational responsibility rather than installation count. Do not conclude that many plugins are slow or directory plugins safe from count or source alone; inspect actual processing, permissions, traffic, and maintainability.
Purpose and success criteria
Define the desired function, users, essential requirements, exclusions, and measurement in one sentence. Avoid duplication if core, theme, hosting, or an existing plugin already meets it.
Check examplePurpose: deliver PDFs only to members; success: unauthenticated URLs cannot retrieve them
Source and maintainer
Use a defined source such as WordPress.org, the developer's official site, or a contracted marketplace. Check author, support, changelog, license, signature, and update distribution path.
Check examplesource, author, support, license, update channel
Compatibility and dependencies
Check Requires at least, Requires PHP, Tested up to, required extensions, theme, plugins, and APIs. Tested up to is not itself a guarantee; test your actual site configuration.
Check exampleWordPress / PHP / DB / theme / dependencies / SaaS
Permissions, traffic, and data
Inventory admin permissions, REST endpoints, cron, file writes, database tables, cookies, personal information, external sends, tracking, and API keys; review the privacy policy and terms.
Check examplecapability, endpoint, table, external host, personal data
Performance and duplication
Measure frontend assets, queries, HTTP requests, cron, cache purges, and admin work. Find duplicate optimization, security, or SEO processing and slow operations rather than relying on count.
Check exampleBaseline → activate → compare page, admin, cron, and logs
Exit, migration, and restoration
Check disable versus uninstall, whether data, shortcodes, blocks, tables, files, and accounts remain, export, migration to alternatives, and rollback-capable backups.
Check exampledisable / uninstall / export / restore / replacement
Classify uses and responsibilities
More plugins in one category are not automatically better. Assign one owner per function and record overlap, external dependencies, and failure impact. These categories describe architecture, not product recommendations.
Input and business functions
form / reservation / commerce / membership
Includes validation, spam controls, email delivery, payments, inventory, permissions, and personal-data retention. Check retry, audit logs, export, and deletion as well as screens.
Display and editing
block / custom post type / gallery / multilingual
If content stores shortcodes, blocks, or metadata, check whether it breaks when the plugin is disabled. Review conflicts with theme features and editor extensions.
Search, sharing, and analytics
SEO / sitemap / schema / analytics / social
Assign owners so multiple plugins do not duplicate title, canonical, robots, sitemap, structured data, or tracking output. Do not promise ranking effects.
Performance optimization
cache / minify / image / CDN / database cleanup
Overlap with hosting or CDN can cause stale cache, double compression, changed script order, or missing admin exclusions. Measure display and server metrics before and after changes.
Security and backup
WAF / login / scan / backup / restore
These add protection but do not guarantee it. Divide responsibilities with server and CDN controls and prepare lockout recovery, backup storage, and restore tests.
Integrations and automation
mail / CRM / API / webhook / scheduled task
Check external outages, rate limits, credential expiry, webhook signatures, duplicate retries, transmitted data, and costs. Disabling a plugin may not delete external accounts or data.
Must-use plugins, drop-ins, and theme-bundled features differ from normal plugins
Must-use plugins load automatically from a special directory and may not be disabled like normal Installed Plugins. Drop-ins such as object-cache.php, host-enforced plugins, and theme-bundled features also exist. Inventory filesystem, hosting settings, and deployment definitions, not just the admin active list.
Information for comparing candidates
Ratings, active installations, and last update alone are insufficient. WordPress.org directory readme metadata helps shortlist candidates, but verify site-specific compatibility, security, support, and the data lifecycle. Directory inclusion guarantees neither defect-free operation nor future maintenance.
| Criterion | Examples to check | How to decide |
|---|---|---|
| Purpose and duplication | required feature / existing owner | Is this the minimum configuration meeting a required need, without duplicating core, theme, hosting, or existing plugins? |
| Runtime requirements | Requires at least / Requires PHP | Does it fit production and staging WordPress, PHP, database, extension, and Multisite requirements and the upgrade plan? |
| Tested scope | Tested up to / changelog | Is the displayed value the developer's tested major WordPress version? Read releases and known issues; do not treat it as a guarantee. |
| Maintenance and support | last updated / support / owner | Consider security contact, issue response, release notes, continuity, contractual support, and handover as well as update frequency. |
| Dependencies and external services | Requires Plugins / API / account / price | Assess the effect of outages, price rises, or expired authentication for parent plugins, add-ons, SaaS, license servers, payments, and mail. |
| Data and exit conditions | tables / options / files / export / uninstall | Check storage, personal data, retention, remnants after deletion, export, migration to alternatives, and access after contract end. |
Ratings and reviews
Read whether reviews apply to the same version, use, and environment and whether support requests are mixed into ratings. Do not assess security or compatibility from average stars alone.
Active installations
Usage scale is context for operating history, not proof of fit or code quality. A large plugin may not suit a small need.
Last updated
A long time without an update warrants checking, but simple plugins may not need changes. Also review supported WordPress versions, issues, vulnerabilities, and maintainer activity.
Free and premium
Paid does not necessarily mean secure or fast. Check license renewal, support period, site count, staging use, limits, export, and post-cancellation behavior in the contract.
Choose automatic, manual, or deferred updates
Both leaving software outdated and immediately updating without tests carry security or compatibility risks. Set a policy per plugin based on criticality, impact, test automation, recovery time, and security information. WordPress supports per-plugin automatic updates; one policy need not fit all.
Conditions favoring consideration of automatic updates
- The change is small and exposed externally, so rapid security fixes are valuable.
- Staging or automated tests, post-update health checks, and alerts are available.
- Complete backups and a fast rollback procedure have been demonstrated.
- The vendor's release quality and compatibility policy are monitored continuously.
- Synthetic monitoring detects failures in critical payment, membership, or reservation paths.
Conditions favoring manual approval and phased rollout
- A major release, database migration, or substantial editor, checkout, or authentication change is included.
- Strong dependencies on the theme or multiple add-ons limit compatible version combinations.
- The update requires cache purging, index rebuilding, external API changes, or manual migration.
- Rollback may compromise database, order, or member-data consistency.
- Changes, required versions, known issues, or support information are insufficient.
A backup becomes an update condition only after restoration is verified
A restore point must include database, uploads, configuration, and external-service state as well as files. Verify restoration elsewhere, time required, and how orders, posts, and applications after the backup will be handled. For urgent security updates, weigh waiting against rollout risk and consider temporary maintenance or WAF controls.
Six steps to isolate conflicts safely
Conflicts can involve themes, WordPress core, PHP, browsers, cache, CDN, external APIs, and server settings as well as plugins. Do not disable production components at random; investigate on reproducible staging or with a limited-impact troubleshooting environment.
- 1
Record symptoms and recent changes
Record URL, role, device, time, action, expected and actual results, HTTP status, console and PHP logs, and recent core, theme, plugin, PHP, or configuration changes. Do not assume a cache purge proves the cause is gone.
- 2
Prepare a restore point and test environment
Verify file and database backups and restoration, then copy to staging with personal data handled appropriately. Put payment, email, webhooks, search indexing, and other external sends in test mode or block them.
- 3
Separate cache and environment differences
Identify browser, page, object, CDN, and OPcache layers and disable or purge only those necessary. Compare PHP version, extensions, memory, theme, and environment variables with production.
- 4
Establish a default-theme, disabled-plugin baseline
On staging, disable normal plugins and switch to a default theme to see whether the symptom disappears. If admin is inaccessible, consider official troubleshooting such as directory renaming; remember must-use plugins and drop-ins can remain.
- 5
Narrow combinations by enabling halves
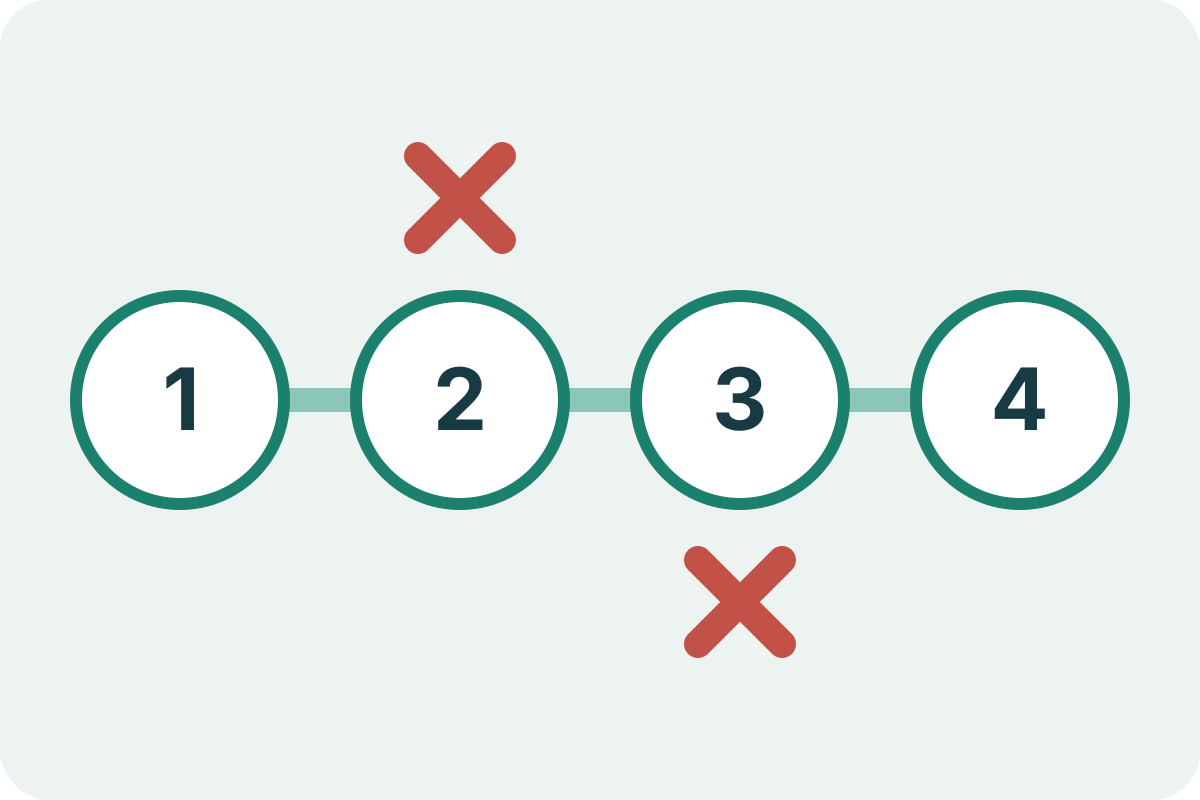
Enable half the candidates at a time to narrow the search. A problem may occur only with A plus B, so record candidates, counterparts, order, and settings rather than testing each only alone.
- 6
Choose a permanent fix and regression test
Choose among configuration changes, version pinning, alternatives, theme fixes, and vendor reports. Keep code changes in managed child themes or custom plugins rather than directly editing core or distributed plugins. Turn reproduction steps into regression tests.
When disabling all production plugins is not acceptable
Use a maintenance window, low-traffic time, canary environment, or Health Check Troubleshooting Mode to limit impact on users. For payments, reservations, or membership, prevent lost transactions and webhooks while stopped. Decide access, records, and recovery decision-makers first.
Update, testing, and recovery basics
Do not treat clicking Update as the whole job. A release includes reading changes, creating a restore point, testing a matching configuration, phased rollout, and monitoring user paths and server state.
1. Inventory and changes
Record plugin slug and version, core, PHP, theme and dependencies, license, automatic-update status, and owner. Read changelogs, advisories, breaking changes, migrations, backup needs, and known issues.
2. Restorable backup
Include database, plugins and themes, uploads, wp-config, and server settings; check storage, encryption, retention, restoration, RPO, and RTO. External SaaS data is managed separately.
3. Update on staging
Update one plugin at a time with production-equivalent versions and settings. Wait for activation hooks, database migrations, cron, cache, and background jobs, and check PHP and application logs.
4. Critical-path tests
Test public pages, login, editor, forms, email, search, checkout, membership, API, mobile, and accessibility. Compare stored data, permissions, status, and performance as well as appearance.
5. Phase production rollout
Share maintenance, backup time, owners, sequence, cache purge, migration, and rollback thresholds. Separate high-impact plugins because bulk updates make causes harder to identify.
6. Monitor after updates
Monitor 5xx, PHP errors, latency, database, cron, queues, email, payment, form conversion, and security events. Do not stop at success status; check later scheduled tasks too.
Rollback is not complete merely by restoring old plugin files
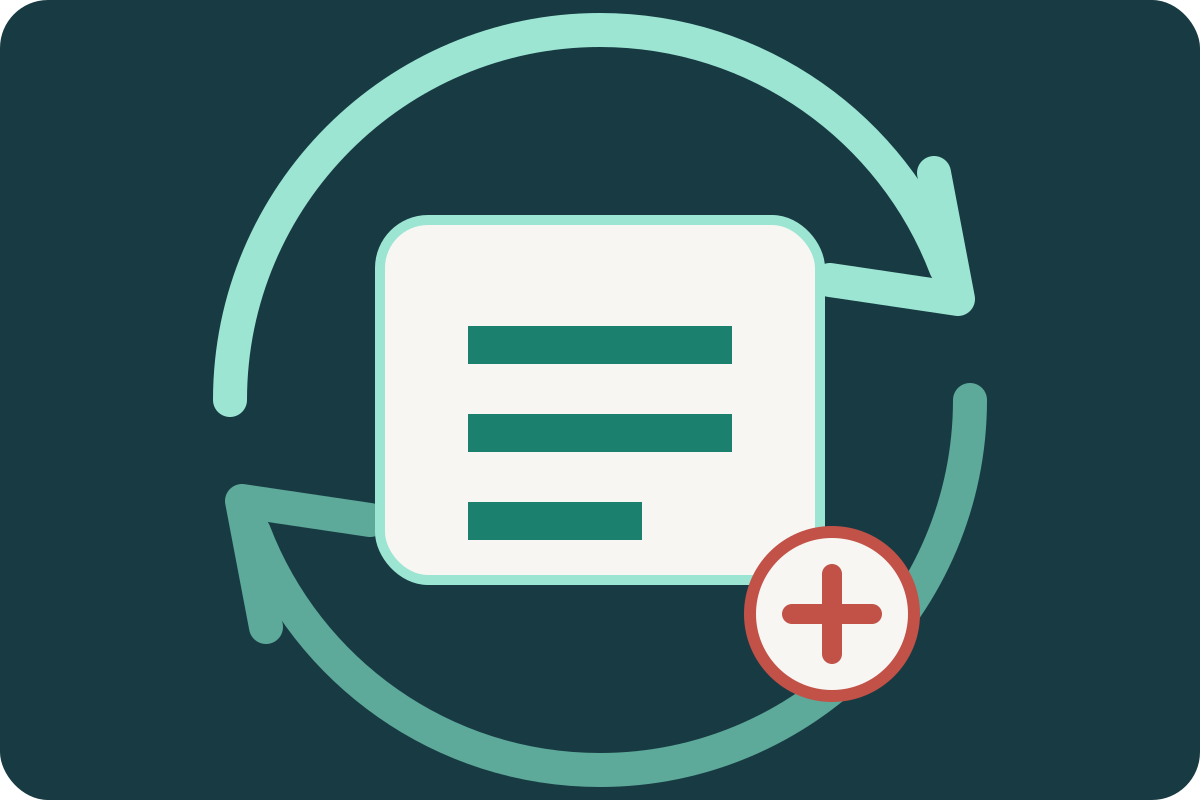
If an update rewrites the database schema or data format, downgrading code alone can leave inconsistencies. Check vendor downgrade support and restore from backup including the database if needed. Decide how to stop, migrate differences, or manually reprocess orders, applications, and posts received afterward.
Diagrams of conflict and update workflows
Because product interfaces change by version, these code-native diagrams show conflict isolation and recovery sequences applicable across plugins rather than a particular interface.
Official WordPress sources used for fact-checking
Definition, management UI, directory metadata, dependencies, conflict isolation, security, and backups were checked against separate sources. Directory rules and displayed information are selection inputs, not safety guarantees.
- WordPress Plugin Handbook: What is a Plugin?
- WordPress Documentation: Manage Plugins
- WordPress Plugin Handbook: Plugin Readmes
- WordPress Plugin Handbook: Detailed Plugin Guidelines
- Make WordPress Core: Introducing Plugin Dependencies in WordPress 6.5
- Learn WordPress: Plugin and theme conflicts
- WordPress Documentation: FAQ Troubleshooting
- WordPress Advanced Administration: Hardening WordPress
- WordPress Advanced Administration: Backups
WordPress plugin FAQ
Are WordPress plugins mandatory?
Not always. If core, theme, or hosting meets the need, no plugin is required. Add one only when the missing function and operational responsibility are clear.
How many plugins are safe?
There is no universal limit. Measure queries, external traffic, cron, assets, permissions, duplicate processing, and maintenance rather than count. Even one plugin can be heavy or unsafe.
Are plugins in the official WordPress.org directory safe?
The directory is an important source, but does not guarantee absence of defects or future maintenance. Verify requirements, updates, vulnerabilities, permissions, traffic, data, and support in your own configuration.
Should I disable all plugins when a conflict occurs?
Do not disable everything indiscriminately in production. Prepare backups and staging, stop external sends, and use a baseline and binary search. Follow official recovery instructions if admin access is unavailable.
Should automatic updates be enabled?
Decide per plugin. Automatic updates can suit low-impact plugins with automated testing, backups, monitoring, and rollback; database migrations or critical paths may warrant phased manual approval.
Is disabling unused plugins enough?
Consider deleting unused plugins, but first check data export, shortcodes and blocks, tables and files, external accounts, licenses, and reinstallation. Disable and uninstall behavior varies by plugin.
Related plugin operations guides
Manage plugins as operational dependencies, not just added code
Plugins normally extend WordPress without editing core files, but add code, permissions, data, external communication, dependencies, and update paths. Define one purpose and owner and check Requires at least, PHP, Tested up to, dependencies, privacy, and data exit. Isolate conflicts from a baseline in a backed-up test environment, including binary search, and treat updates as releases covering changelogs, restore points, staging, critical-path tests, phased rollout, monitoring, and data consistency.
Written and fact-checked by
Finite Field Editorial Team
Our editors covering WordPress development, plugins, maintenance, security, performance, and incident response compared primary and official sources from WordPress.org, Developer Resources, Make WordPress Core, and Learn WordPress.
WordPress plugin architecture and maintenance
Clarify a setup that becomes unstable with each change
If plugins duplicate functions, cannot be updated, have unidentified conflicts or external-data dependencies, or backups have never been restored, we can help organize inventories, responsibility boundaries, staging, tests, monitoring, updates, and rollback.
Discuss custom developmentWe will review the site, contracts, licenses, personal information, external services, maintenance permissions, and recovery needs before advising whether we can help. We do not guarantee complete compatibility, zero vulnerabilities, zero downtime, or particular speed or rankings in advance.