Establish baseline controls before installing a security plugin
WordPress describes security as risk reduction rather than perfect protection. Do not rely on one plugin: reduce attack surface, limit the impact of compromise, and prepare for recovery.
Update the WordPress stack
Maintain core, themes, plugins, PHP, and the web server. Consider removing unused components and combine updates with testing and restore points.
Limit accounts and permissions
Avoid shared administrators; use least privilege, unique passwords, and multifactor authentication. Periodically inventory former employees, contractors, and API integrations.
Protect the server side too
Check HTTPS, SFTP, file permissions, secrets, WAF, and email delivery. A plugin does not replace protection of the OS, PHP, database, or CDN.
Export logs and monitoring
Monitor availability, 5xx, failed logins, added administrators, file changes, outgoing messages, and failed backups; also store logs outside production.
Changing the login URL or adding admin restrictions may reduce attack volume but does not replace vulnerability fixes. These controls can break REST API, XML-RPC, loopback, CDN, forms, payments, or mobile apps, so prepare acceptance tests and a way to disable each setting.
Choose needed functions individually and avoid duplicate controls
Stacking comprehensive products can make login limits, WAF, monitoring, and cache conflict. Identify missing controls and assign one primary owner for each role.
Scroll horizontally to compare purpose, conflicts, and post-installation checks.
| Function | Purpose | Conflicts and side effects | Post-installation checks |
|---|---|---|---|
| Login protection and MFA | Limit brute-force attempts and add protection after password exposure. | Overlapping CAPTCHA, SSO, Basic authentication, and IP limits can lock out legitimate users. | Login, reset, MFA, and emergency disable |
| WAF and request controls | Block known attacks and suspicious requests. | Overlapping CDN, host, and plugin WAFs can misclassify IPs or block forms and APIs. | Forms, payments, API, webhooks, admin, and source IP |
| Malware and integrity scans | Detect known patterns and differences from official distributions. | Consumes CPU and I/O and can flag custom code. Detection alone does not complete cleanup. | Load, exclusions, alerts, comparison with originals, and modification paths |
| Audit logs and change alerts | Connect administrative actions, settings changes, and added users to times and actors. | May over-log secrets; logs on the same server can be lost in a compromise. | Scope, storage, permissions, external forwarding, time, and notifications |
| Backups | Recover from update failures, mistakes, outages, and compromise. | A same-server copy, only database or files, or missing keys or capacity can prevent restoration. | Corresponding time, off-site storage, generations, encryption, and recovery time |
Choose by responsibility and disable paths, not feature count
Check scope, updates, release notes, support, data destinations, load, and remnants after deletion. Avoid duplicating roles in comprehensive products; include host and CDN in the architecture and identify how to disable each control before installation.
Treat backup, isolated tests, phased updates, and monitoring as one process
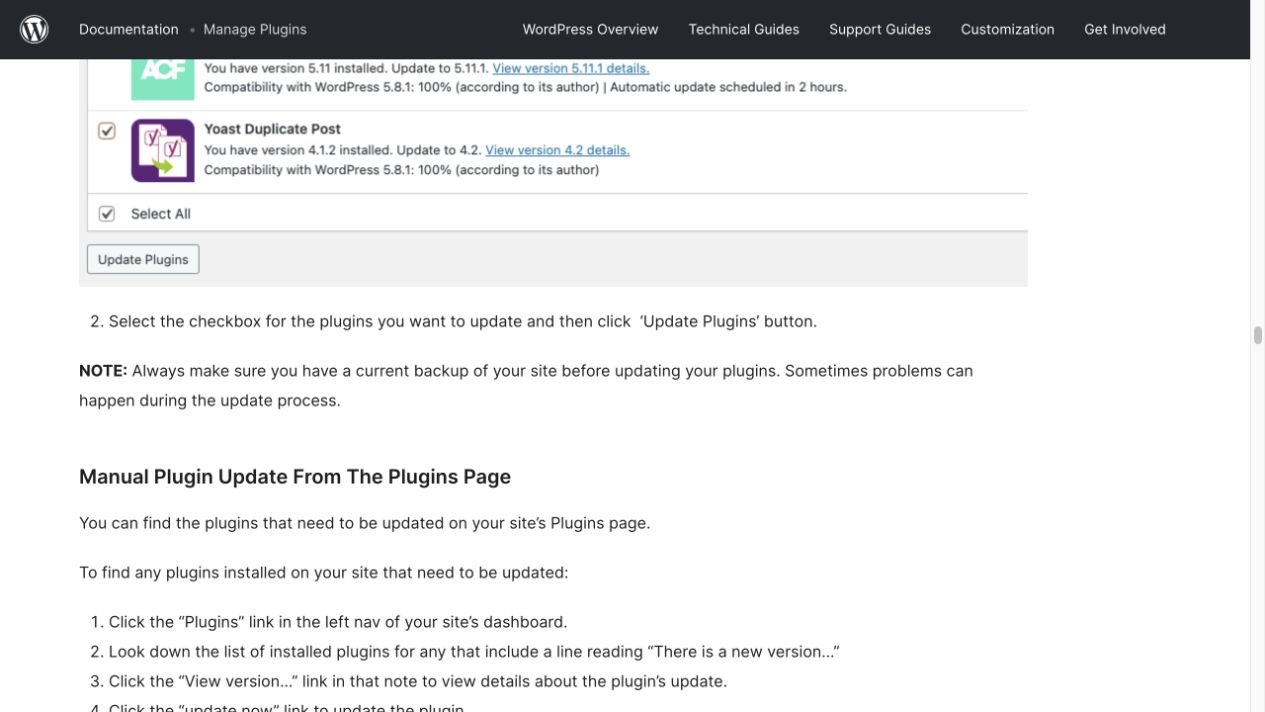
Both leaving components outdated and bulk updating without checks carry risk. Decide on automatic updates by site criticality, staging, monitoring, and recovery time. Verify user tasks, not just success notifications.
- 1
Review changes and impact
Check target versions, WordPress and PHP requirements, security fixes, breaking changes, and known issues with official distributors and providers. Do not update from unknown or modified distributions.
- 2
Capture a same-point restore set
Capture database, wp-content, configuration files, and server-specific settings in the same change window and copy them elsewhere. Check existence, size, readability, and decryption keys rather than relying on a green job indicator.
- 3
Test key functions on staging
Update using PHP, themes, plugins, and cache similar to production. Test login, posts, images, search, forms, email, payments, membership, API, and cron using business workflows, isolating personal data and production sends.
- 4
Roll out gradually and monitor
Apply one change at a time during a low-traffic window and record before/after versions and owners. Check 5xx, PHP errors, response time, forms, login, and integrations immediately and later; stop further changes and roll back if failure conditions occur.
Isolate conflicts one at a time without affecting production users
Layout defects, 5xx, login lockouts, form failures, and latency may arise from combinations of themes and controls. Avoid unplanned mass shutdowns and compare under the same conditions.
- Diagnosis 01
Record symptoms and recent changes
Save URL, time, HTTP status, errors, actions, browser, recent updates, and PHP logs, then reproduce with the same steps.
- Diagnosis 02
Use isolation or Troubleshooting Mode
Prefer staging. Health Check Troubleshooting Mode can show a default theme and disabled plugins only to you.
- Diagnosis 03
Re-enable one component at a time
Check reproduction with a default theme and plugins disabled, then enable required components one at a time. Run the same acceptance tests after each combination of security, caching, optimization, forms, and payments.
- Diagnosis 04
Isolate the suspected cause and choose a permanent fix
Compare configuration changes, updates to fixed versions, alternatives, and provider reports. Do not simply roll back and leave a vulnerability fix unapplied; define temporary controls and a deadline, potentially narrowing public access or adding server-side protection.
If you cannot distinguish a defect from compromise, administrators or files were added unexpectedly, logs disappeared, or suspicious external traffic exists, stop ordinary conflict testing and treat it as an incident. Prioritize access restriction and evidence preservation over indiscriminate deletion or overwriting.
A backup is complete when restoration succeeds, not merely capture
WordPress documentation says a typical complete restore requires both database and files. Assume a backup plugin can itself be affected by compromise, outages, or account termination, and separate storage and restoration paths.
Back up the database
Capture the database, including posts, settings, users, and orders, consistently. For frequently updated sites, decide how to handle changes and transactions during capture and whether orders must pause; record the target restore point.
Back up files and configuration
Include uploads, themes, plugins, mu-plugins, wp-config.php, and web-server settings. WordPress core can be obtained again, but custom code and configuration may differ.
Keep multiple generations off production
Copy to a separate failure domain rather than relying only on the same server or admin account. Check encryption, key storage, access, retention, capacity, deletion protection, and generations from before malware appeared.
Restore into isolation
Restore database and files into an empty environment and check login, display, images, forms, orders, and cron. Record time and procedure so others can recover if the owner is absent.
Do not confuse backup with compromise response
Backups can contain malware or unauthorized administrators. After compromise, investigate entry time, changes, and secret exposure rather than simply restoring the latest generation. Restore a known-good point and fix vulnerabilities; leaving the same entry path invites reinfection.
Distinguish fatal errors from compromise and recover in order
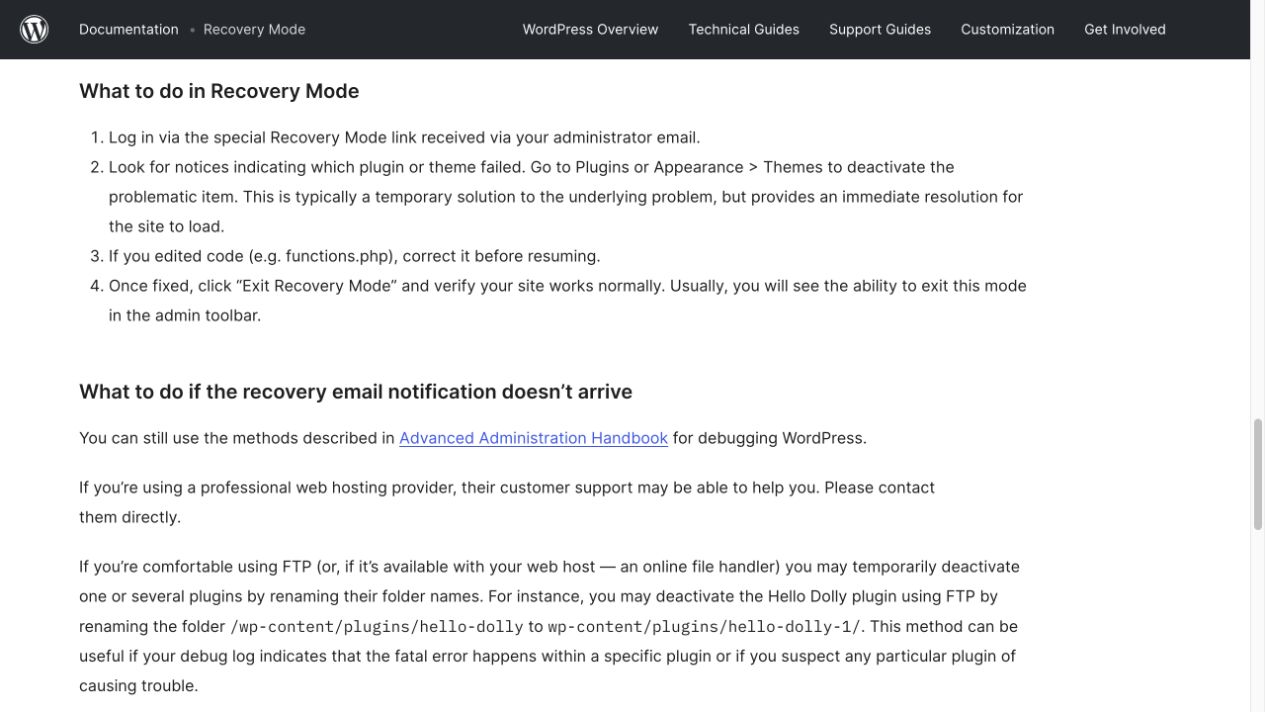
Recovery Mode may let you pause a suspected component after a fatal PHP error. If compromise is suspected, prioritize containment and evidence preservation.
- 1
Stop changes and external impact
Stop additional updates, posting, and orders; limit damage with maintenance, WAF, and access restrictions. Stop integrations with malicious destinations too.
- 2
Preserve logs and state
Preserve discovery time, recent changes, screens, HTTP, PHP, authentication and WAF logs, files, administrators, and external traffic. Avoid mass deletion before investigation.
- 3
Isolate the component
Pause the plugin or theme identified by Recovery Mode. If email does not arrive, consider official instructions, host support, and temporarily renaming the suspect folder.
- 4
Restore and update a known-good state
Restore database and files believed to predate intrusion and update from trusted sources. Check administrators, tasks, mu-plugins, secret keys, and backdoors.
- 5
Rotate credentials from a safe device
Rotate administrator, hosting, SFTP, database, email, CDN, DNS, API credentials and WordPress salts, and invalidate sessions. Check the device first.
- 6
Perform acceptance and prevent recurrence
Monitor key functions, logs, external traffic, search results, and sending. Record cause, impact, recovery, and potential data loss, and assess notification obligations.
Installation, update, and recovery checklist
Do not treat setup as one-time work. Define owners, frequency, evidence, and stop conditions; save site-specific results and update them after configuration changes.
Monthly or periodic checks
- Update status and support deadlines for WordPress, themes, plugins, and PHP
- Administrators, contractors, API integrations, unused accounts, and MFA
- Backup success, off-site storage, capacity, encryption keys, and notification recipients
- 5xx, failed logins, new administrators, file changes, and outgoing email
Before changes
- Review changes, requirements, known issues, provider, and affected versions.
- Capture database, files, and settings at the same point and store elsewhere.
- Test critical tasks and load on staging.
- Record stop conditions, rollback version, owner, contacts, and work window.
After changes
- Login, posts, images, search, forms, email, payments, and API
- 5xx, PHP errors, response time, cron, cache, and WAF false positives
- Monitoring immediately after launch, later, and the next business day
- Record version, person, results, problems, and whether rollback occurred.
Recovery drills
- Restore database and files in isolation and check key functions.
- Verify access to Recovery Mode, file management, and host support.
- Know where external logs, credential inventory, contact lists, and notification decisions are stored.
- Use differences between target and measured recovery times in improvement plans.
Official WordPress sources consulted
The following official sources on baseline controls, updates, conflict isolation, backups, and Recovery Mode were checked July 25, 2026. During actual work, also check current requirements from the host, CDN, and plugin providers.
- WordPress Developer Resources: Hardening WordPress
- WordPress Developer Resources: Security
- WordPress.org Documentation: Manage Plugins
- WordPress.org Documentation: Plugin and themes auto-updates
- Make WordPress Support: Troubleshooting using the Health Check
- WordPress Developer Resources: Backups
- WordPress.org Documentation: Recovery Mode
- WordPress.org Documentation: FAQ Troubleshooting
WordPress security operations FAQ
Are multiple security plugins safer?
Number alone does not determine safety. Overlapping login restrictions, WAFs, scans, and cache controls can cause false positives, load, and admin lockout. Define needed controls, assign one primary owner per role, and review duplication including host and CDN functions.
Should automatic updates be enabled?
Decide per site. Automatic updates can deliver vulnerability fixes sooner but also introduce compatibility issues into production. Enable within your capacity for restore points, staging, notifications, monitoring, and rollback ownership; phase important changes.
Does a backup plugin's success message prove recovery is possible?
A success indicator is insufficient. Verify the database and files form a same-point set, can be retrieved and decrypted from separate storage, and restore into an empty isolated environment with critical functions working. Plan for loss of the backup plugin or server too.
May I delete a plugin directory if I cannot access admin?
Do not delete immediately. Check Recovery Mode, error logs, and host file management. If the cause is known, temporarily renaming a directory may disable it. Deletion can destroy evidence or rollback material; preserve the state and consult a specialist if compromise is suspected.
Is a clean malware scan proof of safety?
No scan can guarantee safety. Unknown malware, malicious database data, stolen administrators, external API keys, altered logs, or configuration defects may be missed. Combine comparison with official files, account and task review, external traffic, logs, credentials, vulnerability fixes, and post-restore monitoring.
Related WordPress operations and recovery guides
A strong setup can be maintained, diagnosed, and restored; feature count alone is not enough
Security plugins supplement missing controls; they do not guarantee complete protection. Base operations on maintained WordPress components, least privilege, server protection, and external logs. Avoid duplicate controls and identify a way to disable each before installation. Create database and file restore points, test in isolation, and monitor production changes one at a time. During failures or compromise, stop changes, preserve evidence, isolate the cause, restore a known-good state, and rotate credentials. Demonstrated restoration informs security decisions.
Editorial and verification policy
Finite Field Editorial Team
We compare official hardening, update, Health Check, backup, and Recovery Mode guidance and organize procedures with stop conditions and rollback.
For conflict, compromise, or restoration decisions
Discuss WordPress security design and recovery
If you cannot access the admin interface, isolate a plugin conflict safely, determine compromise scope, or restore backups, prepare the discovery time, recent changes, errors, configuration, and backup inventory.
Discuss WordPress security and recoveryWe will review the situation and available data before advising whether we can help. We do not guarantee complete defense, full data recovery, zero downtime, rankings, or recovery time in advance.