Start with the smallest plugin setup meeting essential needs
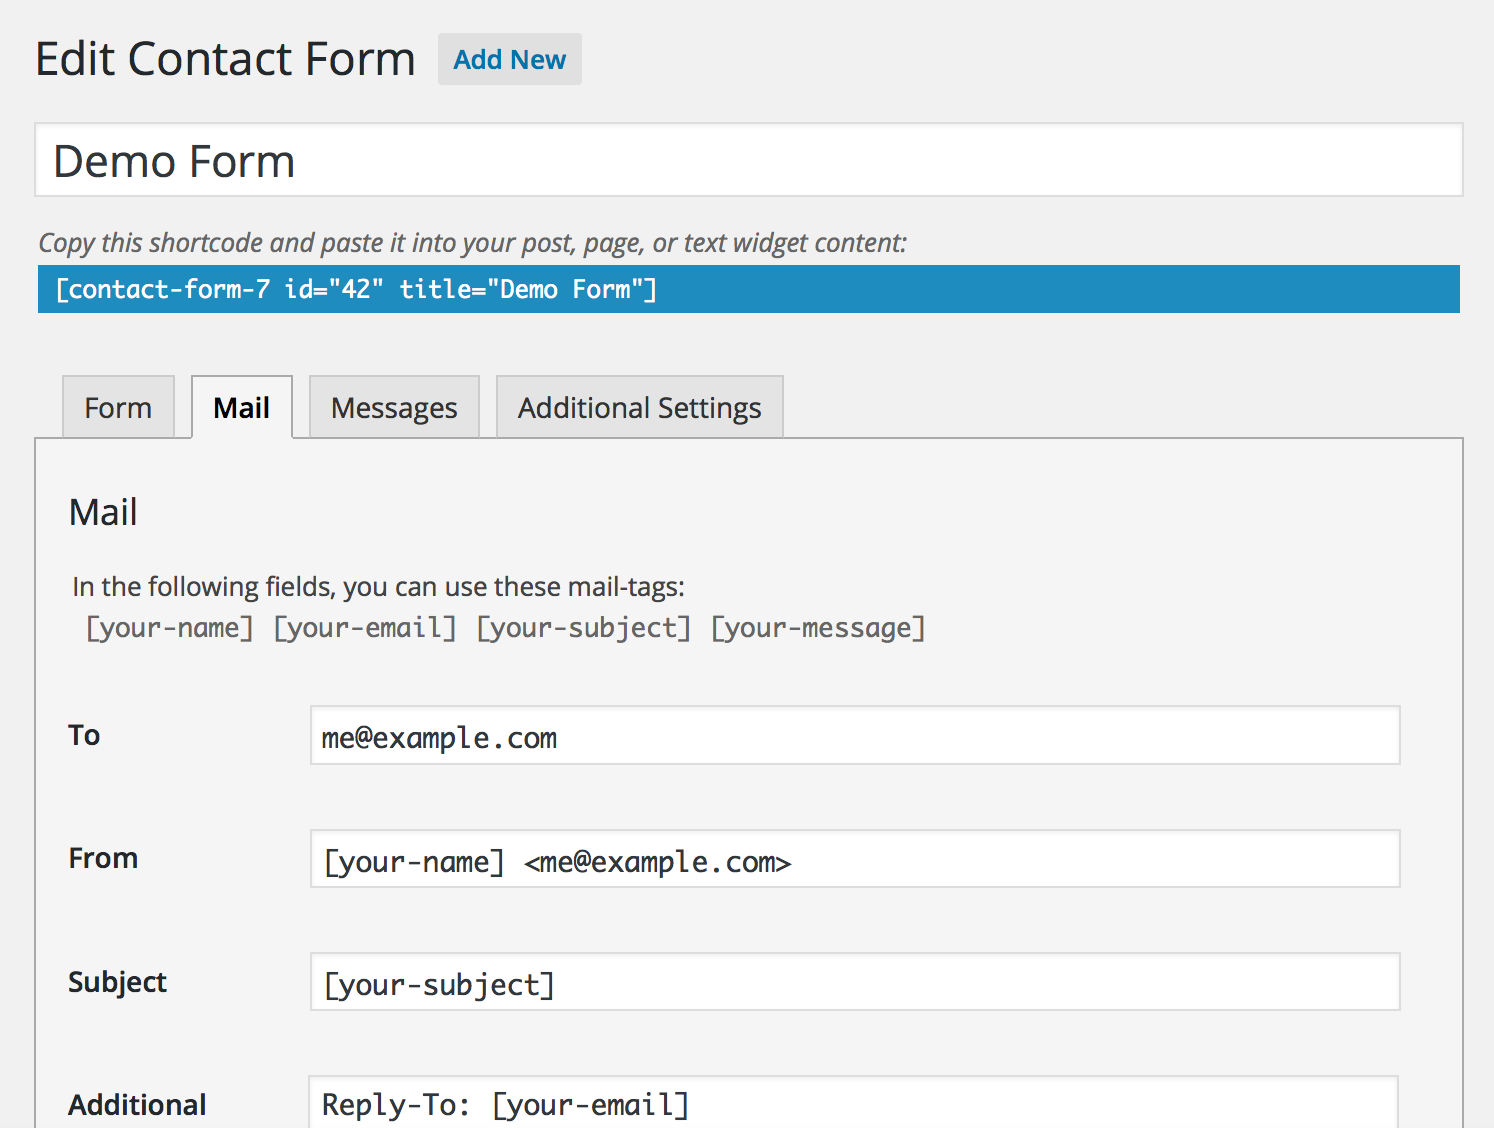
Compare storage, email configuration, spam controls, access, personal-data export and deletion, and records for diagnosing failures rather than name or popularity. Start a general inquiry form with name or company, reply email, subject, and message; add fields only when operational need is established.
Criteria for a first candidate
Choose a maintained option whose configuration staff understand, whose submissions can be reproduced on staging, and whose storage and access can be explained. Prioritize sustainable receipt evidence over free versus paid.
Conditions to avoid
Avoid indefinite storage in an unwatched database, using a visitor's email as From, assuming a success screen proves delivery, claiming CAPTCHA alone is safe, and collecting secrets in free text or attachments.
Ready for publication
Test normal submission, input errors, spam, undelivered mail, and duplicates; reconcile receipts and received mail; and complete deletion tests, access checks, and alternative contact display.
Map personal-data flows first
After submission, values may be copied beyond WordPress to email delivery, databases, CRM, chat alerts, access logs, spam services, and backups. Record purpose and storage for each field and align the privacy policy with implementation.
State what must not be entered
Tell users not to enter passwords, secret keys, card numbers, Japan's My Number identifiers, medical information, or similar sensitive details in an ordinary contact form. If sensitive information is essential, design a separate channel with appropriate authentication, encryption, access, and audit controls.
Scroll horizontally to view the table.
| Processing point | Data to check | Main risks | Pre-launch evidence |
|---|---|---|---|
| Input screen | Fields, attachments, consent, IP and device data | Excess collection, interception, mistaken submission, and entered secrets | Purpose, why required, HTTPS, labels, errors, and notices |
| WordPress processing | Submitted values, nonce, spam decisions, processing logs, and temporary files | Vulnerable extensions, oversized files, unknown storage, and excessive admin permissions | Updates, allowed formats and size, storage settings, and permission list |
| Notification email | Recipients, subject, body, Reply-To, and attachments | Spoofing classification, wrong recipients, forwarding or device copies, and attachment spread | Same-domain From, fixed recipients, actual receipt, headers, and delivery logs |
| Database and CRM | Inquiry text, owner, handling history, and exports | Indefinite storage, broad access, CSV removal, and missed deletion | Retention, least privilege, deletion and export tests, and audit records |
| External services | Spam decisions, mail API, analytics, webhooks, and backups | Cross-border processing, subcontracting, outages, and copies beyond the stated purpose | Transmitted fields, location, contracts, retention, deletion, and outage alternatives |
Choose among five candidates by operating conditions, not rank
No single answer suits every site. Test display with the existing theme, integrations, storage policy, and staff familiarity on staging. This table is a starting point; recheck current free and paid boundaries and external data transmission with official sources.
Scroll horizontally to view the table.
| Candidate | Suitable conditions | Storage checks | Implementation focus |
|---|---|---|---|
| Contact Form 7 | You want to configure forms and email yourself with a small setup. | The default setup does not write personal data to the database. If storage is needed, separately design Flamingo or another destination, access, and retention. | Check same-domain From, Reply-To, mail tags, spam integrations, and actual receipt. |
| WPForms Lite | You want a visual form builder with notification and confirmation settings. | Check per-form storage settings and the viewing and recovery scope of the current license. | Test notification recipients, storage disabling, spam controls, entry deletion, and export. |
| Ninja Forms | You want to manage email, success messages, and storage as separate actions. | Review the Record Submission action on new forms; disable it if unnecessary or define retention and viewers if needed. | Verify each action, including Admin Email, is enabled and check From, Reply-To, subject, and actual receipt. |
| Gravity Forms | You can operate a paid platform with conditional logic and business integrations. | Design storage and deletion for entries, attachments, integrations, and add-ons. | Check licenses, permissions, webhook failures, retries, and personal-data handling by integrations. |
| Formidable Forms | You want to extend entered data into lists, calculations, display, or other business functions. | Because this can become a database application beyond inquiries, define display scope, permissions, retention, and deletion first. | Check public-view exposure, calculations, conditions, export, and free versus paid boundaries. |
Build a safe form with minimal components
Build forms, email, storage, and integrations together on staging rather than directly in production. When replacing a form, monitor old and new URLs in parallel and switch after confirming no inquiries remain unhandled.
- 1
Define purpose and receipt owner in one sentence
Limit the purpose, such as answering quote requests or receiving applications. Assign a recipient and backup, response deadline, holiday handling, and alternative contact. Separate forms for different purposes.
- 2
Reduce required fields
Start with the reply address and subject needed to respond. Before requiring phone, address, department, or attachments, establish why the inquiry cannot be handled without them. Tell users what not to enter in free text.
- 3
Make labels and errors operable
Associate visible labels rather than relying on placeholders. Explain required fields, formats, length, allowed files, and limits before submission; preserve entered values and focus after errors. Check keyboard use and 390px width.
- 4
Check HTTPS and attachment limits
Use HTTPS for the form, confirmation and completion pages, and external APIs. Disable unnecessary attachments; otherwise check MIME, size, count, storage, malware scanning, and whether a public URL is created, not just extensions.
- 5
Explain privacy before submission
Explain fields, purpose, storage, third parties and processors, retention, and contacts in line with implementation. Do not rely solely on a privacy-policy link; state the purpose briefly immediately before submission.
- 6
Test beyond the public URL alone
Test while logged out, on smartphones, with restricted cookies, JavaScript failure, slow connections, and multiple browsers. Check cache, WAF, CDN, and consent management do not block the submission endpoint.
Test email delivery and spam controls separately
A submitted message on screen does not prove delivery to an administrator's inbox. Observe form processing, WordPress mail calls, the host or mail API, and recipient decisions separately. Layer spam controls and test that legitimate users are not rejected.
Email configuration
- Use a fixed From address on the site's domain and put the visitor's address in Reply-To.
- Limit To, Cc, and Bcc to fixed authorized recipients; periodically review former staff and forwarding addresses.
- Check SPF, DKIM, DMARC, and authentication and logs for the SMTP or email API provider.
- Include a receipt number and expected response time in automatic replies without unnecessarily duplicating submitted or sensitive content.
Spam controls
- Layer nonce, timing, honeypot, rate limits, WAF, and content checks according to risk.
- Check data, cookies, external domains, and outage behavior for CAPTCHA or external checks.
- Test legitimate short and foreign-language messages, shared IPs, assistive technology, and restricted JavaScript.
- On rejection, show reasons, retry instructions, and an alternative contact while preventing endless resubmission.
Duplicate and delivery monitoring
- Disable the submit button while processing and test for duplicate receipts after reload or back navigation.
- Reconcile receipt number, time, form ID, and delivery result without increasing personal-data collection.
- Alert on bounces, API and authentication failures, sudden zero receipts, and spam spikes.
- Decide how to recover unhandled submissions from the database or an alternative path if notifications stop.
Manage storage, access, and deletion as one operation
Without storage, undelivered email may lose an inquiry; with storage, responsibility for leaks, export, and missed deletion grows. The safer choice depends on business needs. Balance necessary evidence with minimum retention without relying solely on email or the database.
Before storage
- List every copy in databases, email, CRM, chat, logs, external checks, and backups.
- Separate view, export, and delete rights by role rather than distributing admin rights.
- Set retention and deletion ownership considering law, contracts, and disputes.
During operations
- Do not copy inquiry text to personal devices or unmanaged spreadsheets.
- Log CSV exports and manage storage, sharing, and deletion dates.
- Update the data map after permission changes, plugin updates, or new integrations.
Deletion and disclosure
- Verify identity to prevent disclosure through same names, forwarding, or shared addresses.
- WordPress export and erasure primarily cover WordPress and participating plugins; check external services separately.
- After deletion, check search, trash, email, CRM, logs, and reappearance on backup restoration.
Japan's Personal Information Protection Commission general guidelines describe striving to keep personal data accurate as needed for its purpose and erase it without delay when no longer necessary, including setting retention periods. Specific retention and deletion depend on circumstances; check applicable law and business retention obligations.
Check configuration boundaries in official screens
Inspect actual recipient, sender, and personal-data controls rather than product banners. Interfaces change, so find the equivalent settings in your version instead of memorizing screenshot positions.
Test the complete path from receipt through deletion
Use test personal data, not real production customer data. Reconcile displayed results, stored records, admin notifications, automatic replies, delivery logs, staff handling, and deletion after expiry under the same receipt number.
Normal cases
- While logged out, enter the minimum required fields and submit once.
- The completion message shows receipt, expected response timing, and an alternative contact.
- Administrator notifications and automatic replies reach multiple real inboxes with the correct Reply-To.
- Where data is stored, database or CRM values match the email and only authorized people can view them.
Failure cases
- Safely reject missing fields, invalid formats, long text, HTML, repeated URLs, and prohibited or oversized attachments.
- Repeated clicks, back, reload, and disconnection do not create duplicate receipts or ambiguous completion messages.
- Monitor spam decisions, mail API outages, authentication failures, and storage failures so submissions are not lost.
- Errors do not expose internal paths, SQL, API keys, mail settings, or entered personal data.
Operational cases
- Staff can search and mark submissions handled, while unauthorized users cannot view them.
- Export and deletion requests can be handled after identity verification.
- Data can be deleted after retention expires from the database, trash, email, and external integrations.
- A procedure respects prior deletion records after backup restoration.
Protect receipt and evidence during delivery failure or exposure
Reconfiguring a form without understanding the cause can lose unhandled data or logs. Determine impact and provide an alternative contact before recovery.
- 1
Show receipt status and alternatives
If receipt cannot continue safely, stop the form and show a managed alternative such as telephone or another system and an expected recovery time. Do not encourage indiscriminate resubmission when users are unsure whether a prior attempt succeeded.
- 2
Stop changes and preserve times and evidence
Preserve discovery time, last successful receipt, form settings, update history, delivery, WAF and access logs, database counts, and integration status. Restrict sharing of logs containing personal data.
- 3
Separate receipt processing from delivery
Check success display, database storage, WordPress mail calls, provider acceptance, bounces, and recipient quarantine in order. Reprocess stored but unnotified submissions while preventing duplicate contact.
- 4
Assess possible exposure
Investigate data fields, counts, and periods affected by unauthorized viewing, misdelivery, public URLs, access violations, or external exposure. Promptly assess reporting and individual-notification obligations under applicable law for leaks that may harm rights or interests.
- 5
Retest all scenarios after correction
Do not stop at configuration changes. Repeat normal, failure, spam, delivery, access, and deletion tests; recover unhandled inquiries and record user notices, cause, prevention, and monitoring.
Publication decision checklist
Resolve unclear ownership or evidence before launch.
Interface and safety
- Check HTTPS, visible labels, errors, keyboard use, and 390px.
- Minimize collected fields, attachments, and length.
- Check spam rejection and passage for legitimate users.
Delivery and receipt
- Check From, Reply-To, SPF, DKIM, and DMARC.
- Reconcile administrator notifications, automatic replies, and delivery logs.
- Monitor duplicates, delivery failures, and zero receipts.
Personal information
- Explain all storage and external destinations.
- Apply least privilege to viewing, export, and deletion.
- Record retention, identity verification, and deletion tests.
Primary sources consulted
Checked July 25, 2026. WordPress and plugin features and interfaces change; recheck before installation and updates.
- Contact Form 7: Setting up mail
- WordPress.org: Contact Form 7 privacy information
- WordPress: WordPress Privacy
- Japan Personal Information Protection Commission: APPI Guidelines (General Rules)
- WPForms: How to Create GDPR Compliant Forms
- Ninja Forms: Creating a New Form
- Ninja Forms: Email Action Troubleshooting
- WordPress.org: Flamingo
- WordPress.org: WPForms Lite
- WordPress.org: Ninja Forms
- Gravity Forms official site
- WordPress.org: Formidable Forms
Frequently asked questions
Does a success message mean the email arrived?
No. Even if form processing succeeds, hosting, a mail API, DNS authentication, or recipient filtering can stop delivery. Check actual admin receipt, delivery logs, and bounces.
Is storing inquiries in a database safer?
Not universally. Storage helps recover undelivered inquiries but adds access, export, deletion, and leak-management duties. Balance receipt continuity with minimum retention and define storage, permissions, expiry, and deletion.
Does CAPTCHA complete spam protection?
No. CAPTCHA can be bypassed or reject legitimate users. Combine nonce, honeypot, rate limits, WAF, content checks, and monitoring, and review false positives and externally transmitted data.
May an automatic reply include the full inquiry?
Consider necessity: forwarding, shared devices, and mistyped addresses can copy personal data to others. Focus on receipt number, time, and expected response, and do not return secrets or attachments verbatim.
Does WordPress personal-data erasure delete external-service copies?
Not automatically. WordPress says its tools mainly cover WordPress and participating plugins; third-party services may need separate handling. Check email, CRM, webhooks, logs, and backups individually.
Related operations guides
A form is complete when submissions can be received, protected, and deleted
Collect only necessary information, configure same-domain From and correct Reply-To, test spam controls and real receipt, and operate storage, access, retention, and deletion. Decide readiness from evidence covering receipt, staff notification, user confirmation, and eventual deletion, not just a success screen.
Reviewed by
Finite Field Editorial Team
We distinguish WordPress operations, email delivery, servers, and personal-data responsibilities and organize reproducible release conditions.
Custom WordPress form development and operations
Address delivery failures, spam, and personal-data operations
We can review form settings, email authentication, storage, permissions, integrations, retention and deletion, and recovery of missed submissions to determine needed changes.
Discuss contact-form operationsWe will review the situation, permissions, and service contracts before advising whether we can help. We do not guarantee zero spam, delivery of all email, legal compliance, prevention of leaks, or data recovery in advance.