Prepare certificates, paths, dependencies, and recovery before migrating to HTTPS
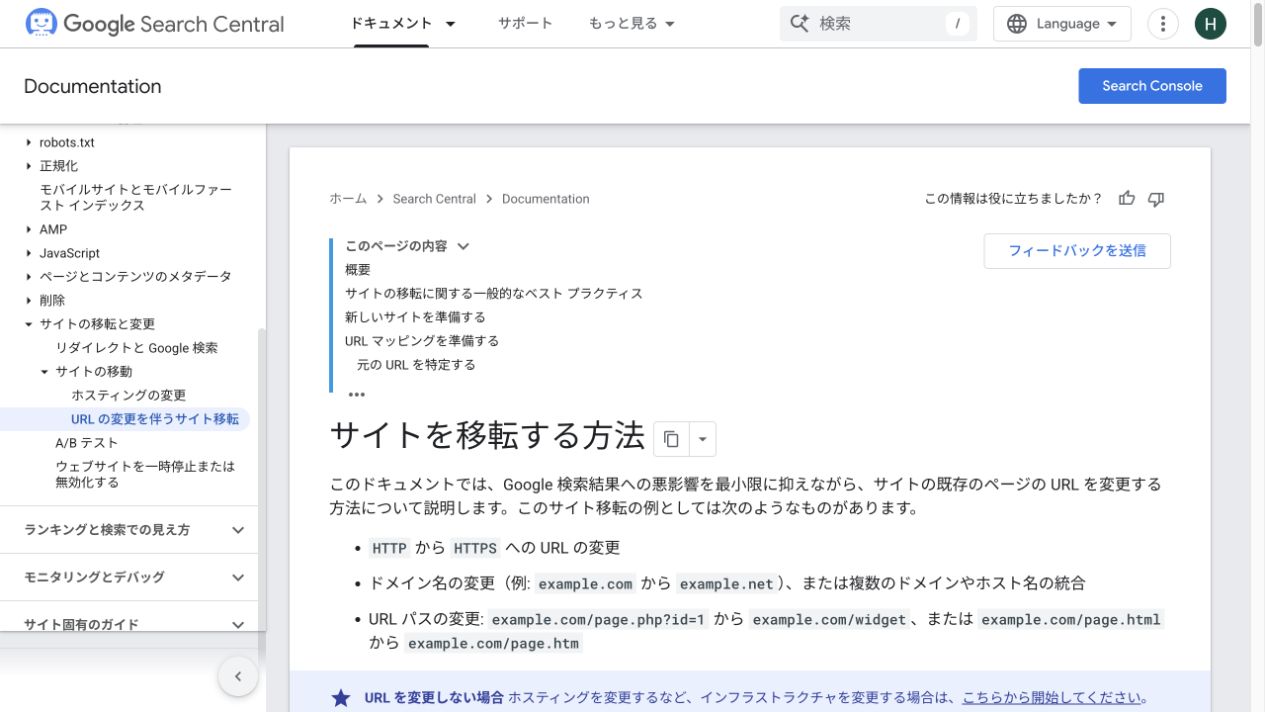
Changing from HTTP to HTTPS is a site move with URL changes. Google describes preparation and testing, URL mapping, redirects, and post-move monitoring. Avoid a simultaneous redesign or CMS migration so that changes can be isolated.
Cover every host with certificates
List the apex domain, www, static delivery, APIs, and administration screens. Check certificate SANs, chains, expiry, automatic renewal, and failure alerts.
Establish TLS termination and redirect ownership
Diagram where TLS terminates and which CDN, load balancer, proxy, or web server owns redirects and www normalization.
Inventory dependent URLs and external integrations
Search templates, CMS content, CSS, JavaScript, images, APIs, iframes, forms, webhooks, OAuth and payment callbacks, and CSP. Decide where hard-coded HTTP references need to change.
Save baseline measurements and recovery means
Record key URLs, status codes, certificates, 5xx responses, forms, payments and login, and search traffic; confirm configuration backups and operating permissions.
Do not redirect all HTTP traffic before key HTTPS workflows succeed. Check certificates, external callbacks, proxy scheme detection, and Secure cookies; handle HSTS last.
Make every entry point reach its corresponding final HTTPS URL in one hop
Map each old URL to its final URL at the page level. Do not redirect everything to the homepage; preserve paths and necessary queries, and avoid multiple hops for www or trailing slashes.
Scroll the table horizontally to compare entry points, responses, destinations, and checks.
| Entry point | Response | Final destination | Check |
|---|---|---|---|
| http://example.com/path?a=1 | 301 or 308 permanent redirect | https://example.com/path?a=1 | Preserve the path and required query and reach the destination in one hop |
| http://www.example.com/path | 301 or 308 permanent redirect | https://example.com/path | Do not split the HTTPS change and host normalization into two redirects |
| https://www.example.com/path | 301 or 308 permanent redirect | https://example.com/path | Install a valid certificate for www before redirecting it |
| https://example.com/path | 200 | Same URL | No self-redirect, loop, or HTTP canonical URL |
| Retired old URL | Permanent redirect if a corresponding destination exists; otherwise 404 or 410 | Only a substantially corresponding page | Do not redirect to an unrelated homepage |
Use 301 and 308 for permanent redirects and 302 and 307 for temporary redirects
For ordinary GET and HEAD requests, 301 or 308 can be used for a permanent move. For requests that must preserve method and body, such as forms and APIs, acceptance-test the behavior of the client, CDN, and application and design with options including 308. Do not decide based on browser display alone: check the response Location, status, method, cookies, and cache.
Use a single server-side redirect and check for loops and omissions
Redirect on the server side rather than with JavaScript or meta refresh. When HTTPS is external but HTTP is internal, incorrect scheme detection can cause loops; define trusted proxies and the detection method.
- 1
Create a URL inventory rather than relying on sample URLs
Create an inventory of old URLs from sitemaps, logs, analytics, Search Console, backlinks, and the CMS. Include nested paths, parameters, www variants, images, PDFs, and nonexistent URLs.
- 2
Implement the rule to the final URL in one place
Combine HTTP-to-HTTPS, www normalization, and path normalization into one rule. Assign responsibilities between the CDN and application, and document excluded URLs and health checks.
- 3
Automatically check status, Location, and redirect count
Check that each old URL reaches its corresponding HTTPS URL in one hop, that the final response is 200, and that the query is retained. Record loops, 5xx responses, 404s, and incorrect redirects too.
- 4
Test POST, APIs, and webhooks separately
Update the destinations for login, forms, payments, webhooks, and APIs to HTTPS. In a test environment, check methods, bodies, authentication, signatures, cookies, and CORS.
- 5
Include caching and monitoring in the migration design
Account for 301 and 308 caching, separate test and production settings, and prepare cache-clearing procedures. Monitor destinations, loops, 5xx responses, and returns to HTTP.
Stop a full cutover if even one redirect loop, 5xx on a key URL, login, payment, or form failure, incorrect redirect to another domain, lost POST, or certificate error is reproducible. Do not stack more redirect rules; record the entry point, each response, Location, proxy headers, and the scheme recognized by the application one hop at a time.
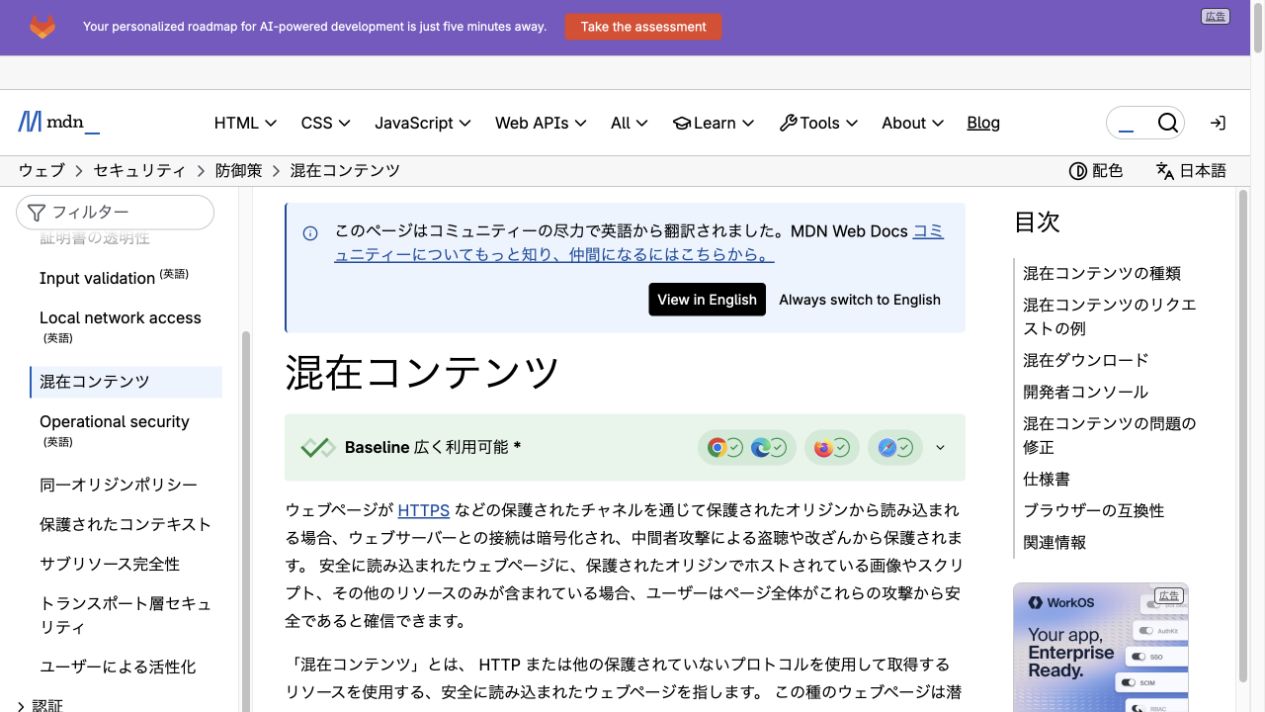
Fix mixed content after confirming that HTTP resources can be served over HTTPS
An HTTPS page loading HTTP images, CSS, JavaScript, iframes, fetch resources, or similar content has mixed content. Do not rely on browser upgrades: change URLs you control to HTTPS and check support for external resources.
Search both source files and the database
Search source code, CSS, JavaScript, environment variables, CMS content, JSON, and email for http://. Explicitly change protocol-relative URLs to HTTPS as well.
Inspect every page type in a real browser
Visit articles, search, login, forms, embeds, payments, and administration screens in a browser. Check Console and Network for HTTP requests, blocking, and CSP violations.
Do not blindly replace text in external URLs
For external URLs, check HTTPS availability, content, CORS, licensing, and SRI. If unsupported, choose self-hosting, an alternative, or removal.
Use CSP to support discovery and defense
Observe violations with Content-Security-Policy-Report-Only before enforcement. upgrade-insecure-requests does not replace fixing stored HTTP URLs.
Follow the cutover sequence from direct HTTPS checks to search-signal updates
Assign owners for changes, monitoring, business checks, and stop decisions. Test during a low-traffic period or on a limited section, and monitor old and new URLs. Search changes take time to appear.
- Cutover 01
Test HTTPS directly before enabling redirects
Check certificates, all hosts, key pages, images, CSS, JS, login, forms, payments, APIs, and administration screens. Inspect robots.txt and noindex as well.
- Cutover 02
Update internal URLs and security attributes
Update internal links, canonical URLs, hreflang, structured data, and sitemaps to HTTPS. Also update cookies, CORS, CSP, and OAuth and payment callbacks.
- Cutover 03
Enable permanent redirects on a limited scope first
On a limited section, check the URL mapping, key workflows, logs, and external integrations. Do not block HTTP in robots.txt; allow crawlers to receive the redirects.
- Cutover 04
Update search, advertising, and external settings
Submit the HTTPS sitemap and check each Search Console property. Update advertising, email, important backlinks, analytics, and feeds as well.
- Cutover 05
Separate immediate, next-day, and ongoing monitoring
Immediately monitor certificates, loops, 5xx responses, and key workflows. From the next day onward, compare HTTP access, 404s, crawling, canonical URLs, indexing, and search traffic.
- Cutover 06
Introduce HSTS in stages after stabilization
Confirm that recovery is possible while keeping HTTPS, and test with a short max-age. Assess includeSubDomains and preload separately.
During an incident, isolate and recover certificates, redirects, applications, and resources
Simply returning to HTTP leaves inconsistencies in cookies, OAuth, HSTS, and search signals. Limit the impact, identify the layer responsible, and first consider fixing the problem while retaining HTTPS.
- 1
Stop further changes and capture the symptoms
Preserve the time, URL, status code, Location, certificate errors, Console, Network, logs from each layer, and recent changes; establish reproducible steps.
- 2
Limit the impact on users
Temporarily suspend or provide guidance for broken payment, login, and form flows while keeping unaffected HTTPS pages available. Do not ask users to ignore security warnings.
- 3
Isolate the cause by layer
Check certificates and SNI, DNS, CDN, TLS termination, redirects, the application's scheme detection, cookies, CORS and CSP, external integrations, and mixed resources in order.
- 4
Revert the smallest necessary change
Restore the problematic redirect, CSP, application, or CDN configuration to a known state. If HTTPS works, stop only the redirects and fix them instead of returning all traffic to HTTP.
- 5
Resume using the same acceptance tests
Recheck the URL mapping, key workflows, mixed content, canonical URLs, and sitemap. Record the cause, impact, recovery, and prevention of recurrence.
For a site with HSTS, returning to HTTP is not a recovery strategy
When a browser remembers HSTS, it upgrades HTTP URLs to HTTPS and certificate errors cannot be bypassed. includeSubDomains and preload extend the scope further. Before enabling HSTS, prepare recovery paths that retain HTTPS, such as certificate renewal, alternative TLS termination, or DNS and CDN changes.
Check HTTPS migration completion against evidence and assigned owners
A page opening is not the sole completion criterion. Record security, user workflows, search signals, operations, and recovery on the same checklist. Do not stop monitoring HTTP access and old URLs immediately after migration.
Before cutover
- Target hosts, certificate SAN, chain, expiry, automatic renewal, and alerts
- TLS termination, redirect owner, trusted proxies, and health-check exclusions
- Old URL inventory, final HTTPS URLs, status codes, and query preservation
- Key workflows, external integrations, cookies, CORS, CSP, and callbacks
- Configuration backups, operating permissions, contact tree, and stop and recovery conditions
Immediately after cutover
- Certificate errors, loops, redirect chains, 5xx responses, and 404s
- Login, forms, payments, search, APIs, webhooks, and email
- Mixed content in images, CSS, JS, fonts, iframes, and fetch requests
- Canonical URLs, hreflang, structured data, robots, and sitemaps
- Monitoring alerts, analytics, advertising, Search Console, and key external links
Ongoing monitoring
- HTTP access and redirect destinations, old-URL crawling, and missed redirects
- Indexing, canonical selection, sitemaps, and search traffic
- Certificate renewal tests, expiry alerts, and TLS configuration changes
- HTTP content introduced by new content and external tags
- Recovery exercises and updates to owners, permissions, procedures, and contacts
Before introducing HSTS
- Stable HTTPS on all target hosts and all required subdomains
- Alternative certificate and TLS termination paths for recovery without reverting to HTTP
- Phased introduction from a short max-age, with monitoring
- Scope of includeSubDomains and private subdomains
- Preload application requirements, long-term effects, and removal procedure
Primary sources and standards consulted
Specifications and recommendations change. During implementation, also consult current official documentation for the CDN, web server, CMS, and authentication and payment services you use.
Frequently asked questions about HTTPS migration
Can I redirect HTTP to HTTPS immediately after configuring the certificate?
First access HTTPS directly and check all target hosts, certificates, key pages, login, forms, payments, APIs, external integrations, and mixed content. Only then enable redirects, starting with a limited scope.
Should I use 301 or 308?
Both are permanent redirects. A 301 is widely used for ordinary page visits. Where a POST or API request must retain its method and body, consider 308 and test the actual path from client to application.
Can mixed content be left alone because browsers upgrade it automatically?
Do not leave it unresolved. Some resources are not automatically upgraded and some types are blocked; future behavior is not guaranteed. Update URLs you control to HTTPS and verify HTTPS support for external resources.
Will search rankings fall after an HTTPS migration?
Rankings may fluctuate during recrawling. Check one-hop permanent redirects, HTTPS canonical URLs, sitemaps, Search Console, and logs.
Should I apply for HSTS preload immediately after migration?
We do not recommend it. Once HTTPS operation across all subdomains and a recovery path that does not return to HTTP are stable, consider a short max-age, includeSubDomains, and preload separately.
Related guides for HTTPS operations
HTTPS migration depends on preparation before redirects and monitoring afterward
Redirect each old URL directly to its final HTTPS URL in one hop. Check key workflows, mixed content, canonical URLs, and 5xx responses, and introduce HSTS only after the recovery path is ready.
Editorial and verification approach
Finite Field Editorial Team
We compare primary sources on search migrations, HTTP redirects, mixed content, HSTS, and TLS, and turn them into a procedure that includes stop conditions and a recovery sequence.
For migrations involving multiple CDNs, servers, and external integrations
Discuss your HTTPS migration and incident recovery plan
If redirects span several layers, payments or APIs cannot be interrupted, or you are concerned about mixed URLs or recovery after HSTS, prepare an architecture diagram, URL inventory, external integrations, and certificates.
Discuss HTTPS migration and recoveryWe will assess whether we can help after reviewing your architecture and operating conditions. We do not guarantee uninterrupted service, search rankings, crawl completion dates, continued operation of external services, or complete prevention of incidents.