
This article contains no advertisements or affiliate links. Definitions and technical specifications prioritize official RFC, IANA, ISC BIND and Google materials. For actual configuration, also check the instructions of your registrar, DNS, email and hosting providers.
The key to a DNS change is not to 'wait 48 hours', but to check authoritative DNS, caching DNS and live services separately. Time alone cannot fix incorrect authoritative DNS data or inconsistent name-server delegation or DNSSEC.
DNS connects names and services. Verify changes in three stages.
DNS handles more than IP addresses, including mail destinations, delegations, authentication information and certificate issuance controls. After changes, check authoritative DNS, user-side caches and the operation of web, HTTPS and email services in order.
| What is DNS? | A distributed system for managing and retrieving IP addresses, mail destinations, delegations and authentication information associated with names |
|---|---|
| Common records | A, AAAA, CNAME, MX, TXT, NS, SOA, CAA, PTR, SRV, SVCB and HTTPS |
| Key points for changes | Save the current zone, change only the intended records and keep the old environment and rollback procedure |
| Verify the change | Check all authoritative servers → multiple recursive resolvers → web, HTTPS and email |
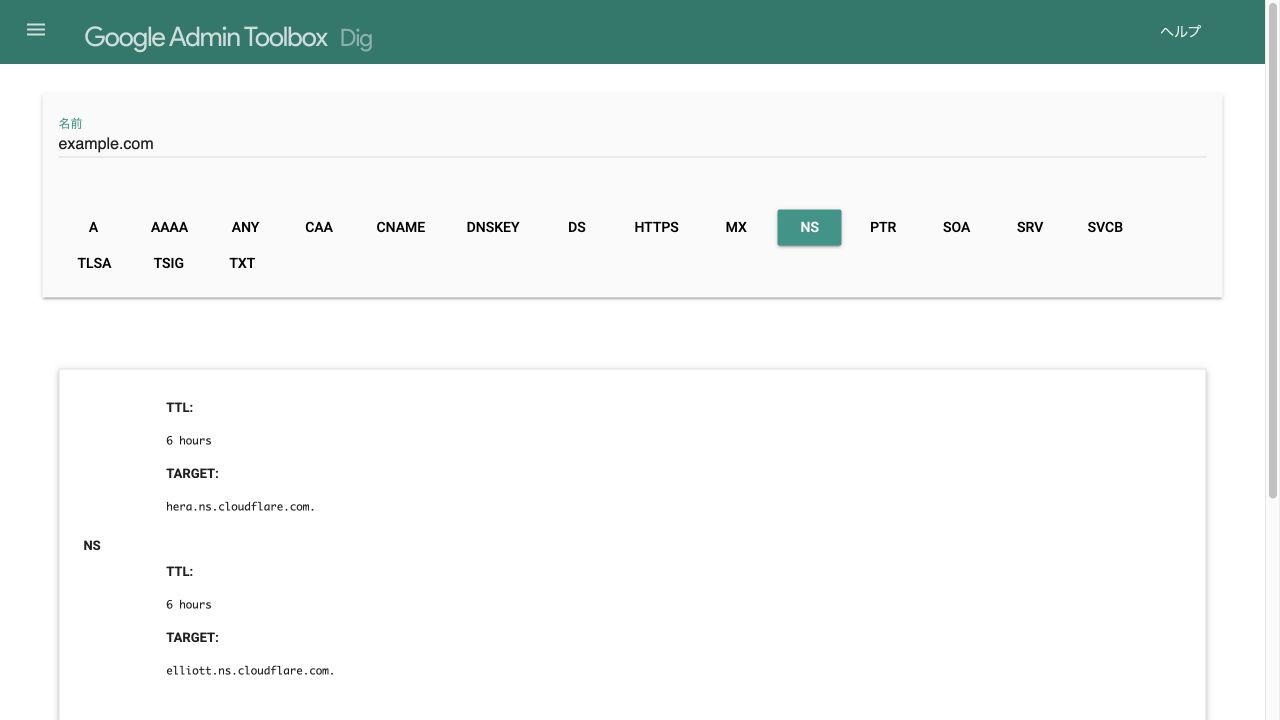
| Common checking tools | dig, PowerShell Resolve-DnsName, nslookup and Google Admin Toolbox Dig |
| Main sources checked | July 29, 2026 |
What is DNS?
The Domain Name System (DNS) uses a hierarchical domain namespace and distributed database to query information associated with names, such as IP addresses, mail destinations, delegations and verification data.
For example, when you enter https://example.com/guide/ in a browser, DNS primarily handles example.com as the host name. The path /guide/ and page content are not handled by DNS; the web server reached after name resolution handles them.
Without DNS, users would need to remember IP addresses whenever they connected to websites or mail servers. If a service moved servers and changed its IP address, it would also have to tell each user the new destination. By separating names from destinations, DNS lets operators change their setup while keeping the same name.
What DNS can answer
Examples include web IP addresses, mail destinations, authoritative name servers, domain ownership verification and permitted certificate issuers. Answers depend on the record type queried.
What DNS alone does not guarantee
Whether a website exists at the destination, its TLS certificate is valid, its application works and mail can be received are separate checks. Even with correct DNS, a 500 or certificate error can occur.
Check the role behind 'DNS server' and 'name server'
The terms are used broadly, but an authoritative name server that returns official data and a recursive resolver that searches and caches answers on a user's behalf have different configurations and failure causes. State which name and type you queried and which server you asked.
How does DNS name resolution work?
A device does not query every DNS server directly each time. Normally the operating system's stub resolver asks a recursive resolver such as a company, ISP or public DNS service. If a valid answer is cached, the process ends there; otherwise, the recursive resolver follows the DNS hierarchy.
Enter a URL
The browser needs an IP address for the host name.
The device queries DNS
The operating system or application asks its configured recursive resolver.
Follow the hierarchy
Without a cached answer, the resolver looks through root, TLD and authoritative DNS servers.
Return the answer
The recursive resolver returns the authoritative answer to the device.
Connect to the server
The browser starts an HTTPS connection to the returned destination.
Five key roles in name resolution
.com and .jp are examples of TLDs; the root server refers queries to their responsible servers.A cache hit avoids tracing from the root every time
A recursive resolver with a valid cached answer returns it without querying authoritative DNS again. This reduces DNS load and latency, but also explains why different users can see old and new answers immediately after a change.
Common DNS record types and their roles
For a DNS change, avoid the vague phrase 'change the domain settings' and specify which FQDN and record type will change, and the old and new values. Deleting MX or TXT during a web migration, or overwriting a web A record during a mail migration, can happen when changes are made without examining the whole zone.
Scroll the table horizontally to compare purposes, cautions and checks.
| Type | Primary role | Configuration cautions | Checks after changes |
|---|---|---|---|
| A | Maps a host name to an IPv4 address. | Changes the destination for web or API traffic. Use provider-specified values for a CDN or load balancer. | Check the A answer, HTTP response, HTTPS certificate and virtual host. |
| AAAA | Maps a host name to an IPv6 address. | If only A changes while AAAA points to the old environment, IPv6 users alone may reach the old site or encounter an outage. | Query AAAA separately and test actual traffic over IPv6. |
| CNAME | Maps a name to another canonical name. | The final target must resolve. Other record types generally cannot coexist at the same name. | Check the CNAME, the target's A and AAAA records, and the service itself. |
| MX | Identifies receiving mail servers and their priorities. | A destination is normally specified as a host name, which also needs A or AAAA records. Do not shut down the old environment prematurely. | Check priorities, destination names, actual sending and receiving, delays and bounces. |
| TXT | Stores text for uses including ownership verification, SPF, DKIM and DMARC. | Several uses can share a name. Avoid replacing all existing TXT records in the control panel. | Check the exact host name and text, and verify email authentication results. |
| NS | Identifies authoritative name servers for a zone. | Check parent delegation separately from NS records in the child zone. Changes affect the whole zone. | Check parent delegation, each authoritative server's responses, SOA serials and all records. |
| SOA | Provides zone administration information, a serial and values used for negative caching. | Helps determine whether updates have reached multiple authoritative servers. | Check SOA serials on all authoritative servers and the SOA in an NXDOMAIN response. |
| CAA | Restricts which certificate authorities may issue certificates. | Misconfiguration can prevent legitimate certificate issuance or renewal. Use the values specified by the service. | Check the CAA answer, certificate renewal logs and ACME errors. |
| PTR | Used for reverse lookups from IP addresses to names. | Usually configured by the IP address owner or cloud provider, not solely in your ordinary zone. | dig -x or a similar command performs a reverse lookup; for mail, also check forward and reverse consistency. |
| SRV | Identifies a service's destination host, port, priority and weight. | Uses a service-specific name format. Applications that do not support it will not use it. | Check SRV values, the destination host's A and AAAA records and actual client behavior. |
| SVCB / HTTPS New connection information | Provides service connection information such as alternate endpoints, ALPN, ports and IP hints together. | HTTPS is an SVCB-compatible type for HTTP. It relates to features such as HTTP/3 and ECH, but requires support from clients and providers. | Check HTTPS and SVCB answers, A and AAAA records, ALPN and the actual HTTPS connection together. |
Be careful with CNAME at the zone apex
A standard CNAME cannot coexist with other data at the same name, so it normally cannot be placed at the zone apex, where SOA and NS records are required. Provider features such as ALIAS, ANAME and CNAME flattening are different from standard CNAME. Check the actual response rather than relying on a label.
Understand TTL and DNS change timing
TTL (Time to Live) is the time a recursive resolver or another cache may retain a DNS record. It does not guarantee that every cache worldwide will update within that many seconds after a change. Some resolvers may serve expired data if a refresh fails (RFC 8767). Caches obtained the old value at different times, so old and new answers coexist immediately after a change.
The old TTL matters
Lowering the TTL after a change does not immediately affect caches that already obtained the old value with a longer TTL.
Negative answers are cached too
Answers for nonexistent names or data can also be cached for a time. NXDOMAIN may persist immediately after an addition.
Problems waiting cannot fix
Incorrect authoritative data, NS delegation errors, DNSSEC inconsistencies and differences between authoritative servers do not resolve with time alone.
Why do people say 'up to 48–72 hours'?
That can be a conservative estimate covering provider processing, parent delegation, caches around the world and device or router caches. For diagnosis, however, record the authoritative answers, recursive resolver answers and remaining TTLs rather than relying only on elapsed time.
Prepare before the old TTL expires
If lowering the TTL, do so at least one old TTL before the switch, not immediately beforehand. For example, if the old TTL is 86,400 seconds, lowering it less than 24 hours in advance leaves already-cached old values with a long remaining lifetime. Afterward, restore a TTL appropriate for stable operation.
How to check DNS settings
Do not stop when a web tool shows a new IP. Check authoritative data → external caches → live services to distinguish configuration errors, cached answers and problems outside DNS.
Query authoritative name servers directly
Query every delegated server for the same name and record type and check whether values, TTLs and SOA serials agree. Fix errors here rather than waiting.
Compare multiple recursive resolvers
Compare your usual resolver with another route such as Google Public DNS. For old values check the remaining TTL; for NXDOMAIN investigate negative caching; for SERVFAIL investigate DNSSEC and authoritative responses.
Actually use web, HTTPS and email services
Test key pages, login, forms, APIs, certificates and email sending and receiving. Check A and AAAA, the apex and www, and relevant subdomains separately.
Basic dig examples for macOS and Linux
# Web IPv4 / IPv6
dig example.com A
dig example.com AAAA

# Email, authentication, certificates and current HTTPS information
dig example.com MX
dig example.com TXT
dig example.com CAA
dig example.com HTTPS

# Delegated servers and the iterative query path
dig example.com NS +short
dig +trace example.com

# Compare specific recursive resolvers
dig @8.8.8.8 example.com A
dig @1.1.1.1 example.com A

# Query a specific authoritative name server directly
dig @ns1.example-dns.net example.com A +noall +answer +authoritystatus, ANSWER SECTION, TTL and SERVER, and the queried name and type. Even with NOERROR, an empty ANSWER may mean NODATA: the name exists but has no data of that type.
Checking on Windows
# PowerShell
Resolve-DnsName example.com -Type A
Resolve-DnsName example.com -Type MX -Server 8.8.8.8

# nslookup
nslookup -type=A example.com 8.8.8.8
nslookup -type=MX example.com 8.8.8.8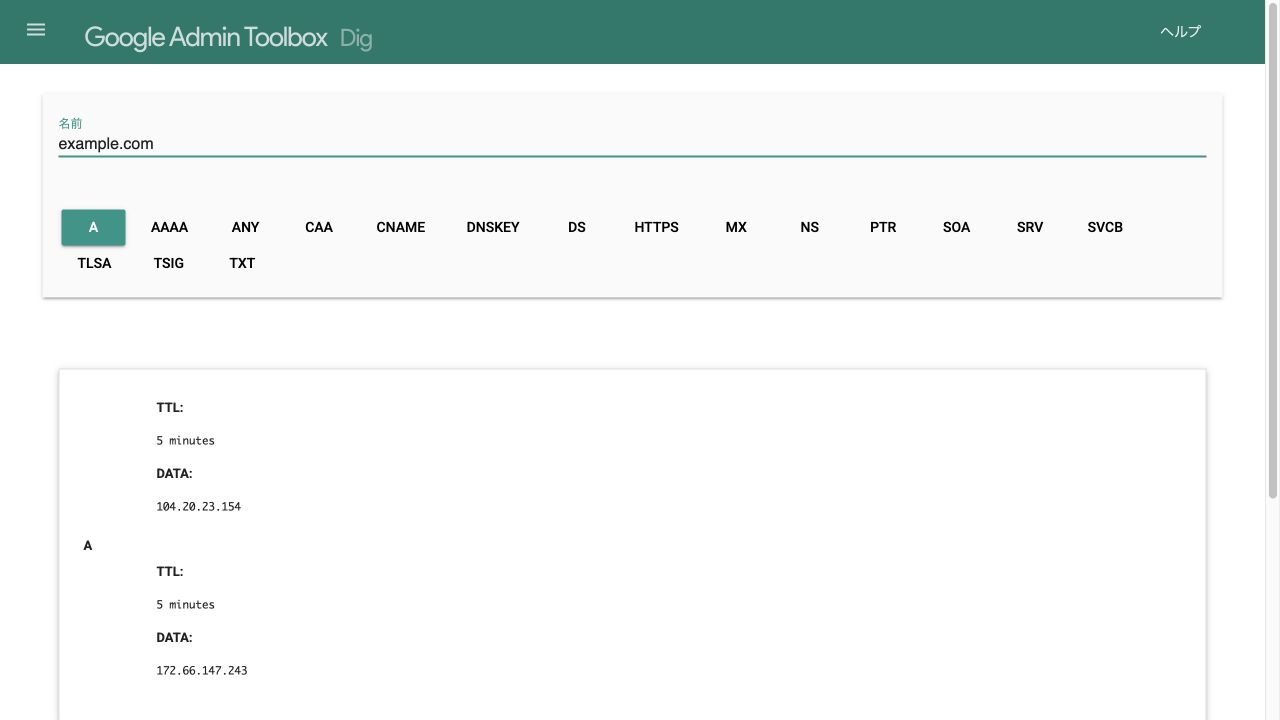
Record six details together
time, query origin, server queried, name, record type, and answer with TTL together. 'It worked on my PC' or 'an overseas check showed the old value' alone does not identify the problematic layer.
How to change DNS safely
For DNS changes, preparation, dependency checks, acceptance criteria and rollback decisions matter more than data entry. The impact of changing one record differs greatly from moving name servers.
Export the current zone
Save all records, including A, AAAA, CNAME, MX, TXT, NS and CAA, plus TTLs, SOA and authoritative name servers. Keep copyable text as well as control-panel screenshots.
Map web, email and authentication dependencies
List records used by the website, email, CDN, SaaS ownership verification, certificates and subdomains. Identify responsible people and contact routes.
Test the new environment before switching DNS
Use a preview URL, hosts file or load-balancer test method to check web, APIs, HTTPS and email first.
Lower TTL sufficiently early if needed
Lower it within provider limits and wait for the old TTL to expire before switching. Lowering it afterward does not shorten existing cache entries.
Change only the intended records
Double-check the FQDN, type, value, priority and TTL. In control panels, @, blank fields, trailing dots and relative names differ between control panels, so follow the provider's notation.
Monitor authoritative DNS, recursive DNS and live services
Record the change time and results, then test critical functions through old and new paths. Keep the old environment running while caches remain.
Roll back when the criteria are met
If authoritative DNS returns an incorrect value, critical functions fail or DNSSEC validation fails, restore the old value or contact your provider instead of merely waiting.
The impact depends on the type of change
| Change | Main impact | Priority checks | Keeping the old environment |
|---|---|---|---|
| A / AAAA | Web, API and subdomain destinations | IPv4, IPv6, HTTPS, key screens, forms and APIs | Keep it until caches converge and logs have been checked. |
| MX | Inbound mail destination | Sending and receiving through both old and new paths; SPF, DKIM and DMARC | Keep it long enough to account for delivery retries. |
| NS | Web, email and authentication information for the whole zone | All new-zone records, parent delegation, glue and DNSSEC | Run old and new DNS in parallel with matching contents. |
| TXT / CAA | Service and email authentication and certificate issuance | Whether existing values were removed and whether required values match exactly | Do not remove old values casually before confirming they are no longer needed. |
Check DNSSEC before moving name servers
If DNSSEC is in use and the parent's DS record does not match the new zone's signature, validating recursive resolvers can return SERVFAIL and the entire domain may become unreachable. Follow the old and new providers' migration procedures to determine when to remove or update DS and start signing.
Troubleshoot DNS by symptom
Do not infer the cause from a DNS error alone; check authoritative servers and recursive resolvers separately. SERVFAIL does not mean a record does not exist. It can mean the resolver could not obtain a valid answer or validation failed.
| Symptom or response | Possible causes | First checks |
|---|---|---|
| NXDOMAIN | The queried name does not exist, delegation or the entered name is incorrect, or a stale negative cache remains. | Query authoritative DNS directly; check spelling, zone, SOA and negative TTL. |
| NOERROR with an empty answer | Possible NODATA: the name exists but has no record of the requested type. | Check types separately, such as A and AAAA or MX and TXT, and follow CNAME chains. |
| SERVFAIL | DNSSEC validation failure, unresponsive authoritative DNS, inconsistent delegation, timeout or a malformed response. | Compare another recursive resolver with authoritative DNS; check DS, DNSKEY, RRSIG and NS reachability. |
| REFUSED | The server refuses the query under its policy, for example when an authoritative-only server receives a recursive query. | Check the queried server, recursion flag, ACL and intended role. |
| The old IP appears only on some connections | An old cache remains in a recursive resolver, device, VPN or router. | Record the DNS server used on that connection, remaining TTL and both A and AAAA answers. |
| Authoritative name servers return different values | Zone transfer or distribution is inconsistent, one update failed, or servers use different zones. | Compare the record and SOA serial on every authoritative server. Fix distribution rather than waiting. |
| DNS is correct but the site will not open | A web server, firewall, virtual host, application or TLS certificate problem. | Check destination IP reachability, HTTP status, certificate name and server logs. |
| The web works but mail does not arrive | A problem with MX, the destination's A or AAAA, reception settings, SPF, DKIM, DMARC or stopping the old environment. | Check MX and destinations, actual send bounces, receive logs and authentication results. |
A troubleshooting sequence
If values are wrong or inconsistent, fix the zone or distribution before waiting for caches.
Record remaining TTL, negative caching, DNSSEC validation and the server queried.
Investigate layers outside DNS, including HTTP, TLS, mail, APIs, databases and authentication.
Do not stop investigating at 'DNS is propagating'
When old and new answers coexist, the server queried and TTL can show whether caching explains the difference. Incorrect authoritative answers, bad delegation or DNSSEC validation failures do not resolve with time.
DNSSEC, encrypted DNS and HTTPS records
Several DNS-related mechanisms improve security, but protect different things. Similar names do not make them interchangeable.
DNSSEC
Uses signatures to verify DNS data origin and integrity; it does not encrypt queries. A DS mismatch during delegation can lead to SERVFAIL.
DoH / DoT
Encrypts DNS communication between a device and recursive resolver using HTTPS or TLS. Encryption does not correct a wrong authoritative record.
SVCB / HTTPS
Records that advertise alternate endpoints, ALPN, ports and other connection information through DNS. They can also distribute settings for HTTP/3 and ECH, standardized in 2026.
ECH as of 2026
ECH (Encrypted ClientHello) encrypts part of the TLS ClientHello, strengthening protection for destination names previously visible in plaintext. RFC 9848 defines how clients obtain necessary configuration using the ech parameter in SVCB or HTTPS records.
ECH works only when the DNS provider, CDN, browser and server support it. Rather than guessing records, use the settings supplied by your service and test the HTTPS record together with actual connections.
Adding a new record does not automatically make a site fast or secure
Clients without support use conventional A or AAAA records. Incorrect SVCB or HTTPS settings can cause connection failures, so follow your provider's official instructions and prioritize fallback and monitoring.
Frequently asked questions about DNS
Are DNS and a name server the same thing?
No. DNS is the overall system for distributed management and retrieval of information associated with names. A name server responds to DNS queries. Authoritative name servers hold official data; recursive resolvers search and cache answers for users.
How many hours does a DNS change take?
There is no universal time. It varies with the old TTL, when caches obtained the old value, negative caching, parent delegation and provider processing. First verify that every authoritative server returns the correct value, then compare multiple recursive resolvers.
Will changing an A record also stop email?
Changing a web A record does not necessarily stop email if MX points to another host and its A and AAAA records remain unchanged. It can affect mail when the MX destination depends on the changed name, mail runs on the web server, or the migration involves SPF, DKIM or DMARC. Test actual sending and receiving.
Can a CNAME be configured at the root domain?
A standard CNAME normally cannot be placed at the zone apex because other data, such as SOA and NS, cannot coexist at the same name. Provider features such as ALIAS, ANAME and CNAME flattening differ from standard CNAME. Follow the service and DNS provider's instructions.
Is the change complete when a web tool shows the new IP?
Not necessarily. Check every authoritative name server's answer, multiple recursive resolvers, and actual functions such as web, HTTPS and email in order. A web tool shows the result from one query origin to one destination.
Are DNSSEC and DNS over HTTPS the same?
No. DNSSEC verifies the origin and integrity of DNS data. DNS over HTTPS and DNS over TLS primarily encrypt communication between a device and recursive resolver. Neither directly guarantees a web server's TLS certificate or application security.
Will restoring the old DNS value immediately restore service?
Rollback is necessary, but caches that obtained the wrong value may retain it for the remaining TTL. Save the old values accurately, keep the old environment available, and monitor convergence while recording the change and rollback times, queried servers, answers and TTLs.
Primary sources and official tools checked
The following standards and official documentation are the basis for DNS definitions, terminology, caching, records, DNSSEC, SVCB, HTTPS, ECH and checking commands. For actual work, also consult the latest manuals for your contracted services.
- RFC 1034 — Domain names: concepts and facilities
- RFC 1035 — Domain names: implementation and specification
- RFC 2308 — Negative Caching of DNS Queries
- RFC 8767: Serving stale DNS data
- RFC 8659 — DNS Certification Authority Authorization (CAA)
- RFC 9364 / BCP 237 — DNS Security Extensions (DNSSEC)
- RFC 9460 — SVCB and HTTPS Resource Records
- RFC 9499 / BCP 219 — DNS Terminology
- RFC 9520 — Negative Caching of DNS Resolution Failures
- RFC 9848 — Bootstrapping TLS Encrypted ClientHello with DNS Service Bindings
- IANA — Domain Name System (DNS) Parameters
- ISC BIND 9 — dig manual page
- Google Admin Toolbox — Dig
- Google Public DNS — Troubleshooting
- Google Public DNS — Flush Cache
- IANA — Example Domains
Related guides for DNS changes
Check authoritative data, caches and live services separately
DNS handles more than domain-to-IP mappings: it also manages mail routing, delegation, authentication, certificate issuance controls and current connection information. Save the whole zone and old values before changing only the intended records. Afterwards, check all authoritative DNS servers, multiple recursive resolvers, and web, HTTPS and email in order. For an old value check the remaining TTL; for incorrect or inconsistent values, fix or roll back.
Finite Field Editorial Team
We reviewed DNS standards, current terminology, TTL and negative caching, DNSSEC, SVCB, HTTPS and official tools to create a practical procedure that distinguishes cached answers from configuration errors.